Resumes
August 13, 2026

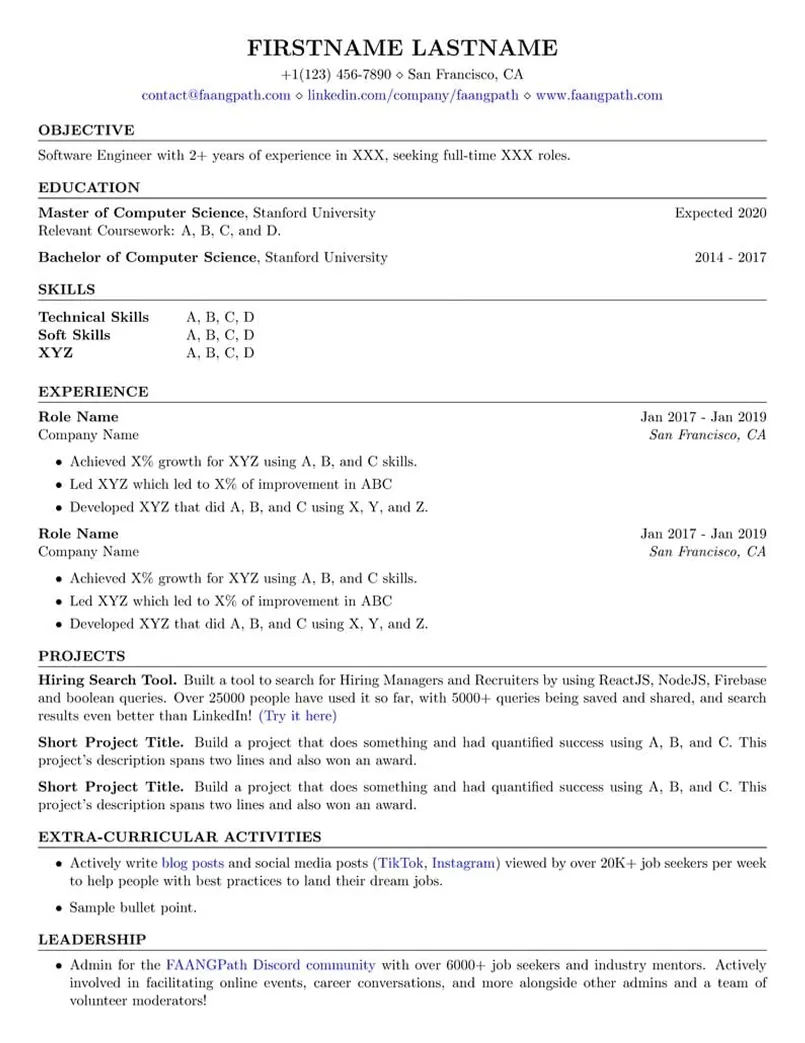

A strong cybersecurity resume should state the environment you protected and what measurably improved. Highlight endpoint, account, or cloud account counts, alert and incident volume, detection and containment times with a before and after, vulnerability closure and patch compliance, and audit or assessment outcomes. List certifications precisely, because Security Plus, CISSP, and GIAC credentials are screened for by name. Say which discipline you work in, since analysts, engineers, consultants, and identity architects share the cybersecurity label and are hired on different evidence. Use the examples below to see how to turn security work into clear, results-focused resume achievements.
Meet Njeri Wanjiku, a fictional cybersecurity practitioner covering 4,200 endpoints across 3 facilities. This example shows a broad defensive role, with containment time, patch compliance, and awareness results all measured rather than asserted.
(256) 555-0117 ◇ Huntsville, AL
njeri.wanjiku@example.com ◇ linkedin.com/in/njeri-wanjiku ◇ njeriwanjiku.com
Cybersecurity practitioner with 10 years defending regulated environments, owning security operations across 4,200 endpoints and 340 servers at 3 facilities. Cut mean time to contain a confirmed incident from 9 hours to 40 minutes, closes 1,400 vulnerability findings a year, and took critical patch compliance from 71% to 98%. A generalist who came up through systems administration.
Coursework in Networks, Operating Systems, Cryptography, and Systems Security.
Also holds CompTIA Security Plus and the GIAC Certified Incident Handler credential.
Containment Time Reduction. Took mean time to contain from 9 hours to 40 minutes by pre-authorising isolation actions and rehearsing them quarterly. The delay had never been technical, it was waiting for permission to unplug something.
Risk-Based Patching. Rebuilt patching around exposure and exploitability rather than raw severity score, which took critical compliance from 71% to 98% while the team actually patched fewer things per cycle.
Awareness Programme. Cut phishing click rates from 22% to 4% by replacing annual training with short monthly simulations and same-day feedback, and by removing the blame from reporting a mistake.
Meet Kazimir Volkov, an analyst working a 24-hour security operations centre. This example is written for detection and investigation work specifically, built on alert volume per shift, false positive reduction, and confirmed incidents led.
(210) 555-0163 ◇ San Antonio, TX
kazimir.volkov@example.com ◇ linkedin.com/in/kazimir-volkov ◇ kazimirvolkov.com
Cybersecurity analyst working a 24-hour security operations centre covering 11,000 endpoints, triaging about 90 alerts a shift. Cut false positive volume 58% by tuning 140 detection rules across 3 log sources, and leads 24 confirmed incident investigations a year including 4 involving credential compromise. Detection and investigation work rather than engineering or advisory.
Coursework in Network Defense, Digital Forensics, Malware Analysis, and Operating Systems.
Also holds CompTIA Security Plus and the Splunk Core Certified Power User credential.
False Positive Reduction. Tuned 140 rules after tracking which alerts had never once led to action across 6 months. False positives fell 58%, which mattered because analysts had started closing a whole rule family without reading it.
Credential Compromise Playbook. Wrote the investigation playbook for credential compromise after 4 cases showed the team was checking the account but not the session tokens or the mail rules left behind.
Triage Time. Took time to first analyst touch from 22 minutes to 5 by reordering the queue on asset criticality rather than alert arrival order, so the environments that mattered were looked at first.
Meet Chidinma Eze, a cybersecurity graduate with Security Plus, a 6-month internship, and competition results. This example shows how labs, capture the flag events, and detection rules that reached production carry a resume before the first permanent role.
(201) 555-0148 ◇ Jersey City, NJ
chidinma.eze@example.com ◇ linkedin.com/in/chidinma-eze ◇ chidinmaeze.com
Cybersecurity graduate seeking a first security role, holding Security Plus and a 6-month security operations internship. Triaged about 40 alerts a day under supervision, documented 22 investigations end to end, and built 8 detection rules of which 5 reached production. No permanent security title yet, so this resume rests on alerts actually worked and rules that shipped.
GPA 3.8; coursework in Network Defense, Digital Forensics, Cryptography, and Secure Programming.
Completed 40 hours of hands-on labs and placed in the top 10% at 2 national capture the flag events.
Home Detection Lab. Built a lab of 6 virtual machines with a log pipeline, then generated attacks against it to write and test detections. Five of the rules developed there were later adapted into production during the internship.
Capture the Flag Competition. Placed in the top 10% at 2 national events across forensics and network analysis categories, and published write-ups explaining the reasoning rather than only the answer.
Packet Analysis Labs. Built 6 teaching labs on packet analysis after watching students struggle with the same concepts, and the course kept them in the permanent material.
Meet Broderick Hensley, 14 months into security after 9 years in IT operations. This example shows the career changer path, where deep knowledge of the estate and a real ransomware recovery become the argument for the move.
(217) 555-0192 ◇ Springfield, IL
broderick.hensley@example.com ◇ linkedin.com/in/broderick-hensley ◇ broderickhensley.com
Entry level security analyst 14 months into a first security role after 9 years in IT operations at the same organisation. Handles about 55 alerts a shift across 3,400 endpoints, closed 320 vulnerability findings, and took ownership of monthly access reviews covering 1,200 accounts within 5 months. Knowing the estate before defending it is the advantage an operations background gives.
Coursework in Systems Administration, Networking, Databases, and IT Service Management.
Also completed a 200-hour cybersecurity programme in 2025 and is working toward CySA Plus.
Ransomware Recovery. Recovered 2 encrypted file servers with 0 data loss because the backups had been restore-tested quarterly rather than assumed. That incident is what prompted the move from operations into security.
Vulnerability Prioritisation. Closed 320 findings in 14 months by ranking on actual exposure rather than severity score alone, which meant internet-facing systems were fixed weeks before internal ones with the same rating.
Access Review Ownership. Took on monthly reviews of 1,200 accounts at 5 months in, work nobody wanted, and found 90 accounts belonging to people who had left or changed roles.
Meet Rania Sarkis, an engineer who builds controls rather than watching alerts. This example covers detection pipelines, response automation, cloud guardrails, and attack surface reduction across 900 cloud accounts.
(703) 555-0125 ◇ Reston, VA
rania.sarkis@example.com ◇ linkedin.com/in/rania-sarkis ◇ raniasarkis.com
Cybersecurity engineer who builds and runs controls rather than watching alerts, owning security tooling across 900 cloud accounts. Cut mean time to detect from 6 hours to 11 minutes by rebuilding log pipelines across 40 sources, and automated 60 response actions that now handle 74% of containment steps without an analyst.
Coursework in Networks, Operating Systems, Distributed Systems, and Applied Cryptography.
Also holds CISSP earned in 2019 and a GIAC cloud security automation credential.
Detection Pipeline Rebuild. Took mean time to detect from 6 hours to 11 minutes by rebuilding ingestion across 40 log sources, most of which had been arriving batched overnight rather than streaming.
Response Automation. Automated 60 containment actions, from account disable to host isolation, with a human approval gate on the destructive ones. Analysts now handle judgement calls rather than repetitive steps.
Attack Surface Reduction. Cut exposed services from 340 to 46 by inventorying what was actually reachable from the internet, which found 200 services nobody had known were public.
Meet Torsten Bergmann, advising 22 client organisations a year. This example shows client-facing advisory work, measured in audit pass rates, assessments delivered, and the ability to put security risk in terms a board will act on.
(410) 555-0159 ◇ Baltimore, MD
torsten.bergmann@example.com ◇ linkedin.com/in/torsten-bergmann ◇ torstenbergmann.com
Cybersecurity consultant advising 22 client organisations a year, from 40-person firms to 9,000-employee groups. Led 30 SOC 2 and ISO 27001 readiness engagements of which 28 passed audit on the first attempt, and delivered 60 assessments producing prioritised roadmaps rather than raw finding lists. Client-facing advisory work, where explaining risk to a board matters as much as finding it.
Coursework in Risk Management, Security Policy, Audit Practice, and Network Security.
Also holds CISA earned in 2018 and an ISO 27001 Lead Auditor qualification.
First-Attempt Audit Record. Took 28 of 30 clients through SOC 2 or ISO 27001 on the first attempt by testing evidence 8 weeks before the audit window rather than assembling it during one.
Roadmap Approach. Replaced finding lists with sequenced roadmaps costed by effort and risk reduction, which is what made 60 assessments actionable. Clients had previously received 200-item spreadsheets and done nothing.
Board Communication. Built a reporting format that expresses security risk in business terms, now used across 22 client engagements a year and adopted internally as the standard deliverable.
Meet Sandhya Venkataraman, an identity architect covering 50,000 identities and 400 applications. This example treats identity as its own specialism, through privileged access reduction, lifecycle automation, and a single sign-on migration.
(972) 555-0186 ◇ Irving, TX
sandhya.venkataraman@example.com ◇ linkedin.com/in/sandhya-venkataraman ◇ sandhyavenkataraman.com
Identity and access management architect owning identity for 38,000 employees and 12,000 contractors across 400 applications. Cut standing privileged accounts from 2,400 to 180 by moving 9 platforms to just-in-time access, and reduced access request fulfilment from 6 days to 20 minutes by automating 240 entitlement workflows. Identity is the specialism, not a subset of general security.
Coursework in Directory Services, Networks, Databases, and Enterprise Systems.
Also holds SailPoint IdentityIQ and Okta Certified Consultant credentials, both kept current.
Standing Privilege Elimination. Took privileged accounts from 2,400 to 180 by moving 9 platforms to just-in-time elevation. The hard part was proving to platform owners that elevation would be fast enough to use during an outage.
Joiner Mover Leaver Automation. Built lifecycle automation that cut orphaned accounts from 3,100 to 40. Movers were the real problem, since people changed roles and kept every entitlement they had ever been granted.
Single Sign-On Migration. Moved 400 applications onto single sign-on over 3 years with no unplanned outage, sequencing by user count so the noisiest failures would have happened on the smallest applications.
Sign up now to access Careerflow’s powerful suite of AI tools and take the first step toward landing your dream job.